Bybit urges immediate Telegram update over reported Android security flaw
Cryptocurrency exchange Bybit published a security advisory warning that an Android vulnerability in Telegram could expose other applications on a compromised device, urging users to install the latest app update immediately.
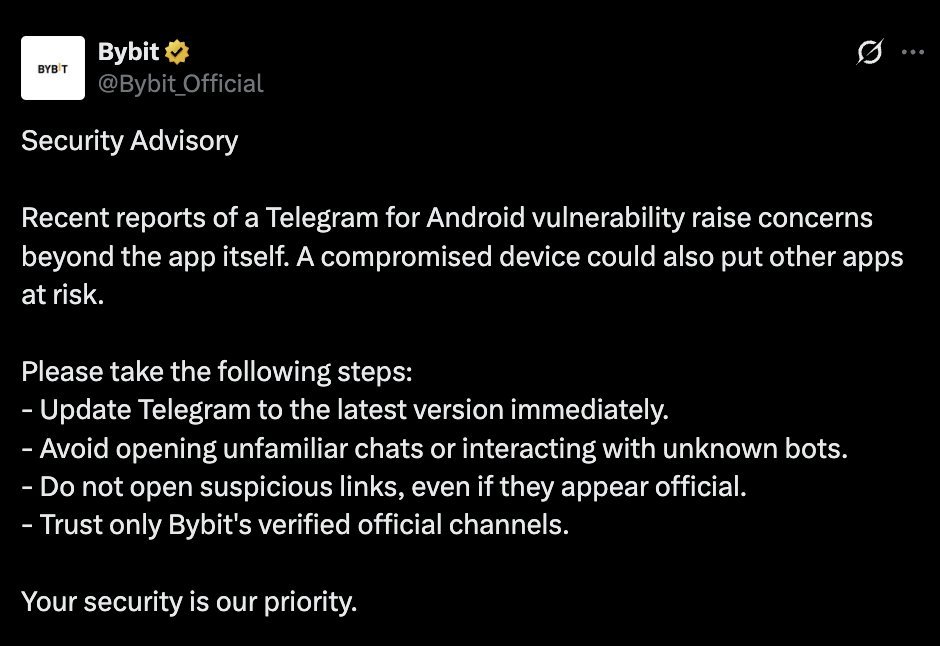
Cryptocurrency exchange Bybit issued a security advisory on November 13 warning users of a reported vulnerability in Telegram for Android, cautioning that a compromised device could put other applications at risk.[1][2][3]
In its advisory, Bybit urged users to update Telegram to its latest version immediately. The exchange also advised users to avoid opening unfamiliar chats, steer clear of interacting with unknown bots, refrain from clicking suspicious links even if they look official, and rely solely on Bybit's verified official channels.[1][3]
The warning follows a disclosure earlier in the week by security research firm V12, which reported a remote code execution vulnerability in Telegram's Widgets feature, according to Wu Blockchain. V12 demonstrated the flaw by using a bot message to trigger the Calculator app on an Android device. Telegram subsequently stated that the issue had been resolved and that a patch had rolled out to users.[3]
The advisory comes amid heightened mobile security vigilance across the crypto industry. On November 10, Binance separately issued a warning regarding an iOS vulnerability called worse_query, which could enable malicious applications to access files from other apps and potentially compromise crypto wallet seed phrases, private keys, and login credentials.[3]
Key facts
- Bybit published a security advisory on November 13 regarding a reported vulnerability in Telegram for Android.
- Bybit warned that an Android device compromised through Telegram could put other installed applications at risk.
- Bybit urged users to update Telegram immediately, avoid unfamiliar chats or unknown bots, avoid suspicious links, and trust only verified official channels.
- Security research firm V12 demonstrated a remote code execution flaw in Telegram's Widgets feature that allowed a bot message to launch an Android device's Calculator app.
- Telegram confirmed the Widgets vulnerability was resolved and rolled out in an update.
- Binance issued a separate warning on November 10 about an iOS flaw named worse_query that could let malicious apps access files containing wallet seed phrases, private keys, or login credentials.
Sources · 3 sources
- DN
DEGEN NEWS@DegenerateNewsPost on X ·
ICYMI: @Bybit_Official WARNS USERS TO UPDATE @telegram "IMMEDIATELY" OVER A REPORTED ANDROID VULNERABILITY - "A COMPROMISED DEVICE COULD ALSO PUT OTHER APPS AT RISK" https://t.co/07AeqQJA3y
Open source - CN
crypto.news@cryptodotnewsPost on X ·
ALERT: Bybit urges users to update Telegram over reported Android vulnerability The exchange warns that the flaw could expose Android devices to compromise, advising users to install the latest Telegram version immediately. https://t.co/j2cjedSbBf
Open source - WB
Wu Blockchain@WuBlockchainPost on X ·
Bybit Warns of Telegram Android Vulnerability, Urges Users to Update Immediately Bybit issued a security advisory on November 13 following reports of a vulnerability in Telegram for Android, warning that a compromised device could also put other applications at risk. Bybit urged users to update Telegram to the latest version immediately, avoid unfamiliar chats and unknown bots, refrain from opening suspicious links, and trust only verified official channels. Earlier this week, security research firm V12 disclosed a remote code execution vulnerability in Telegram’s Widgets feature, demonstrating how a bot message could launch the Calculator app on an Android device. Telegram subsequently confirmed that the vulnerability had been fixed and the update rolled out to users. Separately, on November 10, Binance warned of an iOS vulnerability known as worse_query that could allow malicious apps to read files belonging to other applications, potentially exposing crypto wallet seed phrases, private keys and login credentials.
Open source